Credit Overage Handling and Hard vs. Soft Limit Design
Hard limits block usage instantly; soft limits let customers overage and settle up later.
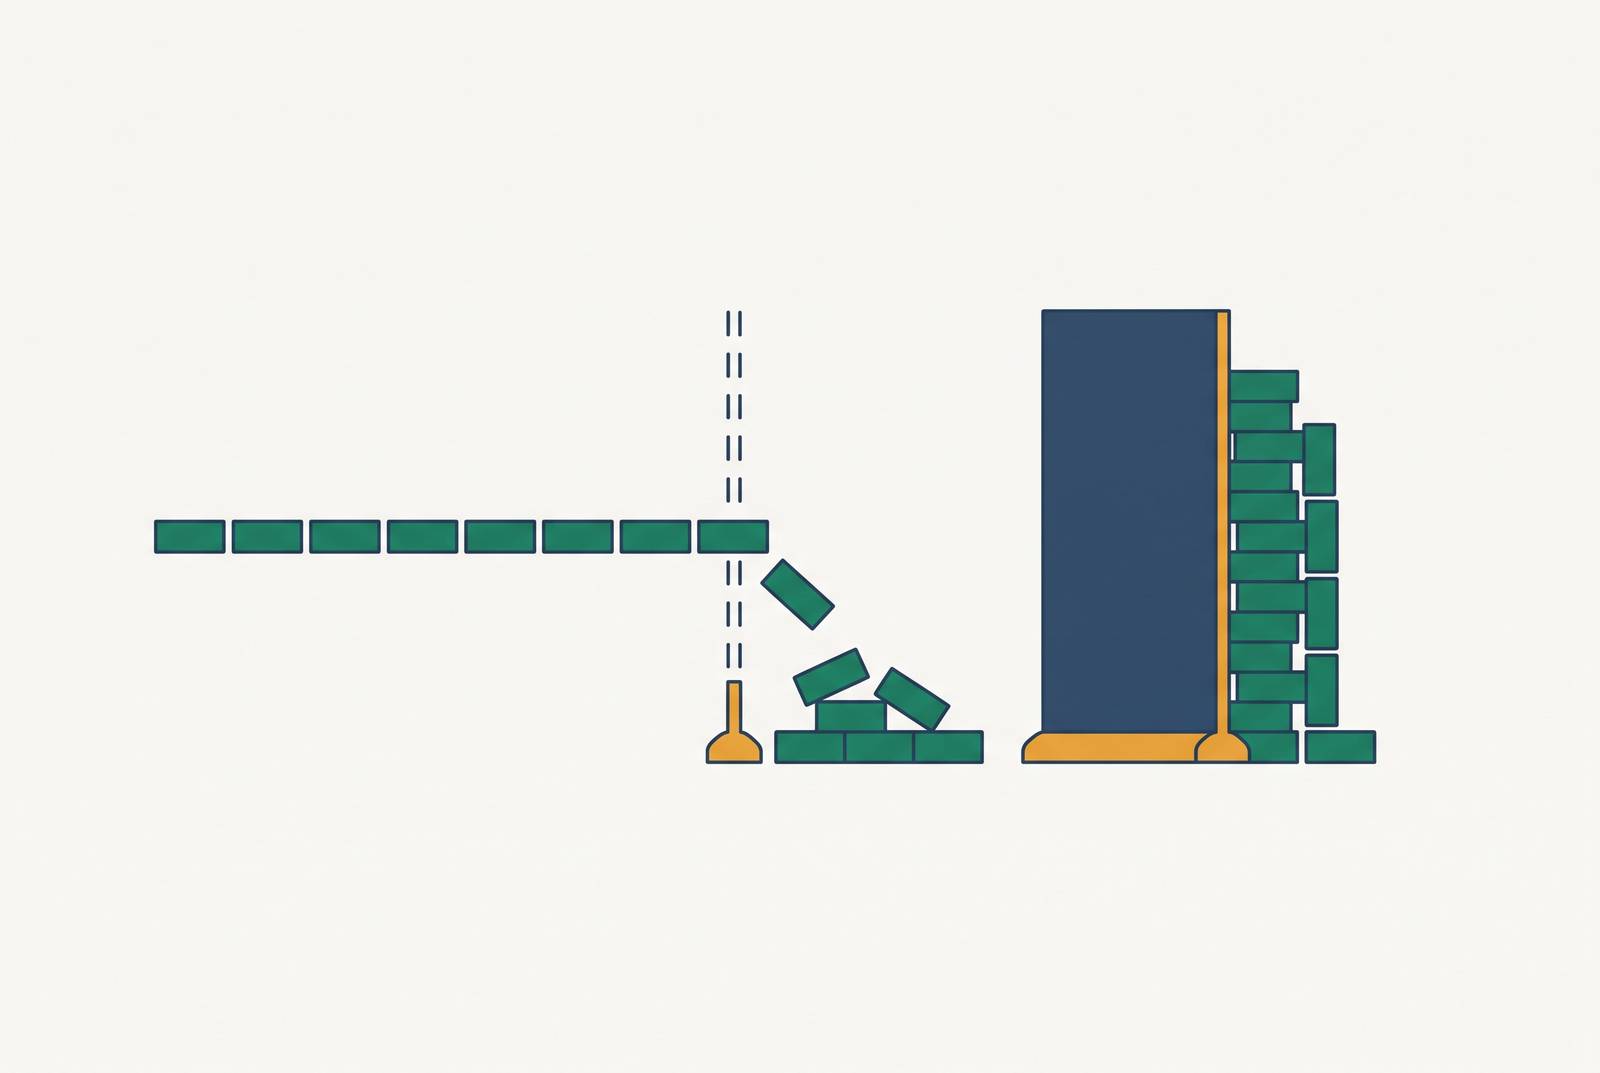
Hard depletion blocks the request the second the balance hits zero. The application can throw up a paywall, an upgrade flow, or a top-up prompt, but no usage proceeds until the customer does something first. Soft depletion lets usage continue past zero: the system logs a negative balance or an overage entry, and billing settles the difference at period end or once a threshold trips. Neither approach is cosmetic. Each is an enforcement posture that dictates what the system checks at request time, what the ledger has to record, and what the customer actually feels the moment their balance disappears.
Credit pricing differs from pay-as-you-go billing in a way that matters here: the purchase happens before the usage. Enforcement has to be live, checked during the request itself, not reconstructed afterward from a usage log. Retrospective billing can tolerate a delay. Prepaid credit enforcement cannot, because the whole premise of the model is that the customer already paid for a fixed amount of consumption.
A third path gets confused with soft limits but isn't one: automatic top-up, or auto-recharge. Instead of letting the balance go negative, the system purchases and grants a new credit block the moment the balance drops below a set threshold, so the customer never actually sees zero. This runs on its own billing logic and its own entitlement checks, separate from either hard or soft depletion. Most mature products don't pick just one of these three paths. They run all three at once: hard cutoffs on a free tier, soft overage on a paid tier, auto-recharge as an opt-in upgrade. That means the system needs configuration-driven enforcement, not a single global rule baked into the code.
The ledger and data model that make enforcement possible
A single number representing "current balance" cannot support any of this. What's actually needed is a ledger of discrete credit events, where every credit block carries its own amount, its own expiry date, its own cost basis, and a category tag distinguishing paid credits from promotional ones. Each block also needs its own depletion behavior, because a promotional grant might expire on a much shorter timeline while a paid purchase carries a longer shelf life.
The ledger has to be append-only. Every grant and every debit gets written as an immutable event, and the current balance is a derived value, computed from the full event history rather than stored and mutated directly. This is what keeps usage data, billing data, and finance data in agreement with each other, and it's what lets support teams reconstruct exactly what happened on a disputed account instead of trusting a single mutable counter that could have been touched by a bug three deploys ago.
Burn order, the sequence in which credit blocks get consumed, is a configuration choice with real financial weight. Burning promotional credits before paid ones is a common convention aimed at preserving the credits the customer directly purchased. Burning credits with the earliest expiration date first prevents accounts from losing balance to expiry through no fault of their own. Neither rule works as a single global default. It breaks the moment an account has a trial grant, a promotional bonus, and a standard purchase sitting in the ledger at once. Burn order needs to be configurable at the plan level and, in some cases, the individual customer level.
Soft and hard depletion demand different things from this ledger. Soft depletion needs the schema to accept negative balances or standalone overage records. Hard depletion needs the enforcement check to happen before any debit gets written at all, blocking the action outright rather than logging it and figuring out the cost later. These are structurally different behaviors, and building for only one makes retrofitting the other painful.
Expiration deserves its own mention, because it's doing double duty as both accounting and psychology. SaaS vendors use credit expiry the same way telecom carriers and credit card issuers use point expiry: as a nudge toward continued engagement and future purchase. When different credit blocks expire on different schedules, which is the norm once promotional and paid credits coexist, the system has to track each grant's expiry independently rather than applying one expiry date to the account as a whole.
A useful stress test for any billing platform under evaluation involves walking it through a plan purchase, a promotional grant, normal consumption, a failed and retried request, a refund, a manual top-up, and a renewal, in that order. A system built correctly produces a clear, traceable balance after each event. A system that can't do this cleanly will eventually produce a balance nobody can explain, usually during a customer escalation.
How concurrent workloads expose the gap between design and production
Here's the failure mode that shows up in production and almost never shows up in a demo: a customer kicks off three agent sessions in parallel, and the balance drains three times faster than the product team modeled. The system checked the balance, approved all three requests against the same pre-debit number, and only then wrote the debits. The overage posts before anyone has a chance to notice, let alone intervene.
AI agent workflows make this worse, not better. Agents run repeated steps, call out to multiple tools, and consume resources at a rate that has nothing to do with how a human clicking through a UI behaves. A plan that looks comfortably profitable under light interactive use can turn upside down the moment a customer delegates a long-running job to an autonomous agent that doesn't pause to consider cost.
The fix is architectural. Enforcement has to happen atomically: checking the balance, approving the action, and debiting the ledger need to happen as a single operation, not as three sequential steps with a gap where two parallel requests can each read the same balance and both get approved. That gap is exactly where the three-parallel-sessions failure lives. Staging environments rarely reproduce the concurrent session patterns that real customers, especially ones running AI agents, generate as a matter of course. That difference separates credit pricing that "works in staging" from credit pricing that holds up under production load.
Scoping credits per seat rather than pooling them across an account is the more defensible default here, not an equally-weighted alternative. Cursor and Fireflies.ai have each adopted variations of per-seat scoped credit models, which limit how much one heavy user can affect the balance others on the team depend on. Pooled models carry real risk by comparison: they need meaningfully stronger billing observability specifically to catch runaway depletion before it turns into a disputed invoice rather than after.
What the choice between hard and soft limits actually signals to customers
Practitioner sentiment on this, drawn from discussion among founders on Indie Hackers, leans strongly in one direction: the last thing a company wants to do is get in the way of a customer using the product, even in excess, especially when the overage doesn't cost the vendor much to begin with. Soft limits are the default worth reaching for, and the discussion treats this as close to settled rather than a coin flip.
The sentiment against surprise charges is even sharper. One practitioner's framing, again from that discussion, put it bluntly: never auto-upgrade or charge overage fees without warning, because it's a fast way to alienate a user who trusted the product with their workflow. The recommended pattern is to notify customers as they approach the limit, then present clear options once they actually hit it, rather than silently converting an overage into a charge the customer never agreed to.
Hard limits are still the right call in specific situations, though, and pretending otherwise would be dishonest. Free tiers are the clearest case: the vendor's cost exposure is real, and the customer hasn't made any financial commitment that would justify extending credit. High-cost workloads are another, where a single runaway session could produce a genuinely damaging overage if left unchecked. And some enterprise accounts, particularly regulated ones or ones operating under strict internal budgets, explicitly want a hard ceiling rather than flexibility.
Soft limits earn their keep in the opposite conditions: when the overage cost to the vendor is small relative to the value of not interrupting the customer, when the product is business-critical enough that an outage does more damage than an unexpected charge, and when the customer has a track record of good-faith usage that suggests they're simply approaching a natural upgrade point rather than abusing the system.
Airgram's reported approach, per the same Indie Hackers thread, splits the difference in a way worth studying: inform the customer once they hit the limit, let them continue briefly, then require an upgrade before further use. That's a graduated response, not an open-ended one, and it preserves continuity without leaving the vendor holding unlimited liability.
The posture itself is a message, whether anyone intends it that way or not. A hard limit says the company protects itself first. A soft limit says the company protects the customer's workflow first and trusts the customer to settle up afterward. Customers absorb that signal even when nobody states it explicitly, and it shapes how they talk about the product afterward. Finance leaders evaluating AI credit plans increasingly expect visibility into consumption and control over how limits are enforced, treating those as operational requirements rather than nice-to-haves.
The alert cadence that separates good limit design from bad
The HubSpot AI Credits Buyer's Guide recommends configuring alert thresholds at 50%, 75%, and 90% of a customer's monthly credit allotment. That progression gives the customer enough runway to actually change behavior before the limit arrives, rather than finding out about it after the fact.
Skip the staged alerts, and even a generous soft limit that never interrupts the workflow will still produce bill shock the moment the invoice lands. The overage itself usually isn't the actual problem. The surprise is.
Part of what makes this hard is that AI credits vary significantly across vendors in how they are defined and measured, which makes forecasting difficult for customers trying to plan spend. There's no industry-standard unit or conversion rate a finance team can reason from independently, no equivalent of "a token costs X regardless of vendor." Vendors that ship real-time consumption dashboards are closing an information gap the customer has no way to close on their own.
Cost previews, showing the credit cost of an action before the customer commits to it, are a proactive version of the same idea, and they cut down on disputes downstream because the customer made an informed choice rather than an accidental one. Rollover and expiry policies need to travel alongside those alerts too: a customer sitting at 90% of their balance with three days left before expiry is facing an entirely different decision than one with three weeks of runway left, and an alert that doesn't distinguish between those two situations isn't doing its job.
Two other approaches from the Indie Hackers discussion handle the grace period differently, and the contrast is instructive. Pirsch notifies the customer when the limit is reached and keeps collecting the underlying data, but blocks further requests after five days if the customer hasn't upgraded, a design that buys the customer time without pretending the limit didn't happen. Shubmakes notifies customers a week ahead of time, and for those who miss that message or simply don't act, blocks the service and shows a prompt inviting them to top up or upgrade to continue. Framed that way, the block reads as a recoverable state rather than a punishment.
This is core work, not optional polish. Customers who can't see their consumption building in real time generate bill shock, and bill shock generates churn and support tickets at a cost that, in most cases, exceeds what it would have taken to build the alerting in the first place.
Unit economics implications of each enforcement posture
Hard limits protect gross margin in the most direct way possible: usage cannot exceed what's been paid for, so there's no unrecovered cost sitting on the vendor's books. That matters most for expensive inference workloads, where one uncontrolled session can rack up a bill that dwarfs what the customer paid for the plan.
Soft limits carry the opposite risk. If overage billing fails, if a customer disputes the charge, or if the billing system mishandles the negative balance at period close, the vendor is the one holding the unrecovered cost, not the customer.
That risk sits inside a pricing environment that's gotten less forgiving. SaaS pricing rose 11.4% in 2025, against G7 inflation averaging 2.7%, a gap of roughly 4.2 times. Vendors pushing prices up that fast need to demonstrate measurable value to justify it, and unresolved overage disputes work directly against that. Nothing undercuts a value story faster than a customer who feels like they got billed for something invisible.
Auto-recharge sidesteps a chunk of this risk by rearranging the sequence: the payment method gets charged for a new credit block before the current one runs out, so the vendor never actually extends credit in the first place. It keeps the margin protection of a prepaid model without the abruptness of a hard stop. That's most likely why it has become the default recommendation for teams that want hard-limit safety without the customer-experience cost.
Expiration functions as its own margin lever, separate from all of this. Credits that expire unused are revenue collected with no corresponding delivery cost, which looks good on paper. But if the expiration policy isn't communicated clearly, it generates churn and refund requests that can offset most or all of that gain. The lever only works paired with the alert cadence described above.
Per-seat scoped credits add one more layer of margin protection, particularly on accounts with lopsided usage: they stop a single high-volume user from consuming an entire account's allocation and leaving teammates locked out. Enterprise buyers, increasingly, are running quarterly ROI reviews, demanding written credit definitions, and asking for consumption reporting broken out by team. Vendors whose billing systems can't produce that level of granularity walk into renewal conversations at a real disadvantage.
How plan tier and use case should determine which enforcement posture to apply
Enforcement posture should be a per-plan configuration, not a single product-wide switch. That's an infrastructure requirement, not a nicety: the platform needs to support different behaviors across tiers, consistently, without custom code for each one.
On the free tier, a hard limit is the only defensible default. Cost exposure is real, the customer hasn't made a financial commitment, and the stop itself becomes a natural upgrade trigger. What matters most here is communicating the limit clearly at signup and inside the product itself, because surprise is the actual failure mode, not the existence of the limit.
On paid tiers aimed at small businesses or growth-stage customers, soft limits paired with staged alerts and a clear upgrade prompt tend to be the better fit. There's a payment relationship already in place, so recovering an overage is operationally realistic, and interrupting a customer's workflow at a critical moment tends to do more damage to retention than the overage charge itself ever would. Auto-recharge with a configurable threshold works well here too, as an opt-in that hands the customer control rather than imposing a posture on them.
Enterprise is where this becomes fully contractual. Some enterprise buyers want a hard cap for budget governance, full stop. Others want soft limits paired with detailed, team-level consumption reporting instead. The billing platform has to support both without bespoke engineering per account, because finance teams now negotiate cap and alert terms before signing, and the vendor able to configure this natively wins the deal that the vendor stuck hard-coding enforcement logic loses.
High-cost AI workloads deserve their own mention, regardless of which tier they sit in. Long-running agents and large batch inference jobs can exhaust a balance before an alert even has time to fire, if the cadence isn't tuned to the actual rate of consumption. Auto-recharge or explicit pre-authorization is often just necessary here, independent of plan tier, because the standard 50/75/90 cadence assumes a pace of consumption these workloads simply don't respect.
None of this replaces good pricing design, either. If the credit allocation is calibrated correctly against the feature that actually drives value, most customers progress naturally through the plan tiers before they ever hit a limit. Limits that fire constantly are usually a signal that the pricing itself is miscalibrated.
Infrastructure requirements that each enforcement posture imposes
Hard limits demand a real-time balance check at request time, and that check, the approval, and the debit all need to happen as one atomic operation. A read-then-write sequence with any gap between the two steps is exactly what produces the concurrent depletion failure described earlier, and no amount of alerting fixes an architecture with that gap built in.
Soft limits demand a ledger that can accept negative balances and standalone overage records, plus a billing layer capable of processing those records correctly at period end or on threshold. Late-arriving events, deduplicating retried requests, and reconciling everything against the ledger aren't edge cases here. They're core engineering requirements that need design attention up front, not patches added after the first billing dispute.
Event ingestion at scale deserves its own line item, because production AI workloads generate usage events at a rate naive implementations simply can't absorb. Purpose-built metering infrastructure needs to process events at millisecond speeds, since batch reconciliation once a day or once an hour isn't a substitute when customers expect to watch their consumption update in something close to real time. Usage collection should be decoupled from the core application, routed through a message queue or a dedicated webhook ingestion service, so a spike in billing events doesn't take down product availability for everyone. Events should also be buffered and batched before they hit the database, both to reduce write load and to smooth out traffic spikes. And idempotency isn't negotiable: if a network hiccup causes a usage event to get sent twice, it has to be counted once, not twice, or every one of these enforcement postures starts producing wrong numbers.
Auto-recharge is the most operationally complex of the three, because it requires the billing layer to detect the threshold crossing, trigger a payment charge, issue the new credit grant, and update the entitlement layer, all before the next request would otherwise fail. That's a multi-step operation that still has to behave atomically from the customer's point of view, even though it touches payment processing, ledger writes, and entitlement checks in sequence.
Alert infrastructure has to be event-driven rather than batch-driven, full stop. A nightly job checking balances once a day cannot fire a 90% alert in time if a customer burns from 80% down to zero in a single afternoon session, which is a completely ordinary pattern for AI agent workloads. Metering and billing aren't two separate problems here. They're one problem, and treating them as though they can be built independently and stitched together later is where most of these systems run into trouble.